A simple take on the ESC13 attack against AD CS (an issuance policy linked to a group), why it's stealthy, how to exploit it, how to detect it, and how RustHound-CE now maps it in BloodHound-CE.
Microsoft Active Directory ADCS BloodHound Red Team Blue Team RustSAFETECH.RED - Blog
Welcome to my blog. I share field reports and hands-on notes from Red Team and Purple Team engagements. I also like digging into Active Directory security techniques and the offensive tools I build in Rust.
-
2026-10-15 ESC13: Being a Phantom Member of a Group
-
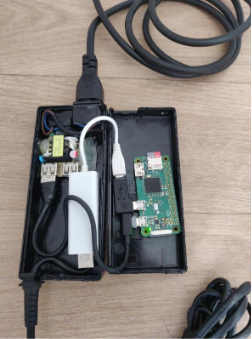
2026-10-12 Physical Intrusion: A Laptop Charger Unlike Any Others!
This article revisits an old presentation I'd put together for colleagues. The idea is to show, from the Red Team side, how to build, configure and conceal your physical implant (dropbox) inside a laptop charger. And from the Blue Team side, to talk about how to detect physical implants.
Red Team Blue Team Hardware Rust -
2026-10-10 The origins of RustHound-CE
A field note on my BloodHound collector written in Rust: why I built it in the first place, and why BloodHound's move to the Community Edition pushed me to release RustHound-CE.
Microsoft Active Directory Rust BloodHound